About · The person behind KROG RULES
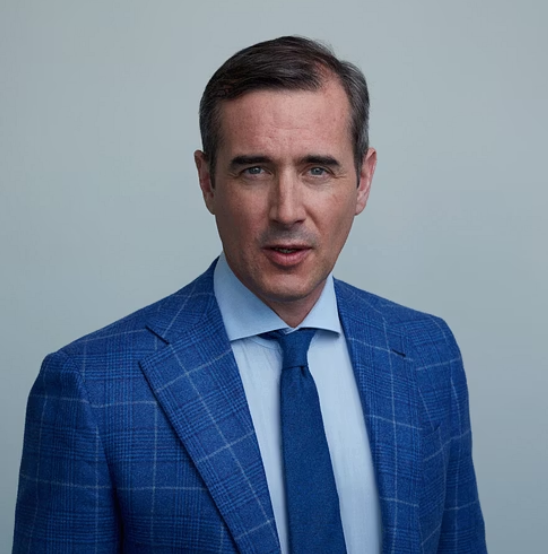
Georg Philip Krog
Lawyer and legal engineer working on data, technology and AI governance — the rules that decide who may know what, who may do what, and who answers for it. I advise organisations, teach practitioners, and build the formal, machine-readable foundations that let those rules be checked rather than merely asserted.
01 · Background
Law, standards and engineering
Two decades between legal practice, research and building software — with the same question throughout: how do you state a rule precisely enough that a machine, an auditor and a court can all read it the same way?
Practice
Legal and regulatory
Privacy, data protection and intellectual property law — including work with WIPO and, more recently, with MLL Legal on data, technology and AI regulation for enterprises.
Building
RegTech and legal engineering
Co-founder of Signatu, building consent, transparency and policy infrastructure; and founder of the KROG Network, where the advisory, training and rule-language work comes together.
Standards
Research and standardisation
Studies and research in Oslo and at the Max Planck Institute, Stanford and Harvard, and work on machine-readable vocabularies for rights, consent and policy in W3C and European standardisation contexts.
02 · Expertise
Practice areas, services and competences
Stated in controlled vocabularies rather than prose — so that what I do can be read, compared and checked by a machine as well as by a person.
Practice areas
What law
- Privacy Lawdata-protection
- Artificial Intelligence Law / Regulationai-regulation
- Technology Lawtechnology
- Cybersecurity Lawcybersecurity
- Digital Identity & Trust Services Lawdigital-identity-trust
Legal services
What kind of work
- Advisory Serviceadvisory
- Regulatory Complianceregulatory
- Data Protection Officer servicedpo-service
- AI Governance serviceai-gov-service
Working languages
Norwegian Bokmål (native) · Norwegian Nynorsk (fluent) · English (fluent) · Swedish, Danish, German (intermediate)
Legal competences
Level-graded, bridged to e-CF
- Data Protection Law (applied)Expert
bridges e-CF E.8 · E.9
- AI Act ComplianceExpert
bridges e-CF E.3 · E.9
- AI & Data Risk Assessment (DPIA/FRIA)Expert
bridges e-CF E.3
- Technology & Data Contract DraftingExpert
bridges e-CF B.5 · D.8
- Regulatory Engagement & EnforcementExpert
bridges e-CF E.9
- KROG Rules & DPS FormalisationExpert
bridges e-CF A.5 · B.1
Competence levels are claimed, not third-party assessed.
AI Act actor contexts
Roles I advise on
Provider
Develops an AI system or GPAI model, or has one developed, and places it on the market under its own name.
Deployer
Uses an AI system under its authority in a professional capacity.
Authorised Representative
EU-based entity mandated by a non-EU provider to act on its behalf.
Importer
Places on the EU market an AI system bearing a non-EU entity's name.
Distributor
Makes an AI system available on the EU market without being provider or importer.
Operator
Umbrella term covering provider, deployer, authorised representative, importer and distributor.
Informative — supports planning, not a legal determination.
KROG certifications
Knowledge modules
Machine-readable consent records (ISO/IEC TS 27560)
krog:Knowledge/ISO27560
Passed — KROG certifiedOnline privacy notices and consent (ISO/IEC 29184)
krog:Knowledge/ISO29184
Passed — KROG certifiedRecords of Processing Activities (GDPR Art. 30)
krog:Knowledge/ROPA
Passed — KROG certifiedData Protection Impact Assessment (GDPR Art. 35)
krog:Knowledge/DPIA
Passed — KROG certifiedPersonal data breach notification (GDPR Art. 33–34)
krog:Knowledge/BreachNotification
Passed — KROG certifiedEU AI Act compliance (Regulation (EU) 2024/1689)
krog:Knowledge/AIActCompliance
Passed — KROG certified
Modules are binary — held or not held. No bar admissions on file; KROG registers bar status, it does not issue it.
03 · Contact
Work with me
For advisory engagements, in-house training or course enrolment, write to hello@signatu.com.